

Key Points:
- Mobile communications compliance applies to business communications, regardless of whether the message is sent through SMS, WhatsApp, iMessage, Teams, or another channel.
- Off-channel messaging creates compliance risk when business communications cannot be appropriately captured, preserved, supervised, or produced.
- A written policy banning personal messaging apps does not by itself prevent employees from using those channels for business communications.
- Compliance requires more than message capture. Retention, legal holds, supervision, search, and production also need to be addressed.
- A compliant architecture does not necessarily require every record to reside in one repository, but disconnected systems can make governance, investigation, and regulatory production more difficult.
- Archon Data Store can provide a governed archive for captured mobile communications, supporting policy-driven retention, legal holds, immutable preservation, audit logging, and search across connected enterprise records.
Regulators no longer care which app your employees use to talk to clients. What they care about is whether business communications are properly identified, preserved, supervised where required, and available when regulators or other authorized parties need them. That shift explains almost everything happening in mobile communications compliance today.
For years, firms treated this as a channel problem: approve email, restrict WhatsApp, hope nobody texts. That approach has quietly stopped working, because the recordkeeping obligation does not disappear simply because a business communication moves to a different messaging application or device.
What Is Mobile Communications Compliance
Mobile communications compliance is the process of identifying, capturing, retaining, supervising, and producing business-related communications conducted through mobile devices and messaging applications in accordance with the rules that apply to the organization.
SMS, iMessage, WhatsApp, Signal, Teams chat, and similar applications can create compliance obligations when they are used for regulated business communications. The important distinction is the nature of the communication, not simply the channel.
A firm’s recordkeeping obligations depend on the type of business being conducted, the applicable regulatory requirements, and whether the communication falls within the records that must be maintained.
A corporate-issued phone does not automatically make a communication compliant, and a personal phone does not automatically place a business communication outside the firm’s obligations.
That is why off-channel communication has become such a persistent compliance issue. Employees may move a conversation from email to text, from a corporate application to a personal messaging application, or from a firm-issued device to a personally owned phone. The firm’s recordkeeping and supervisory responsibilities do not simply disappear because the communication moved.
This isn’t confined to financial services, though that’s where the obligation is most codified. Healthcare organizations coordinating care over text face privacy and security requirements around protected health information. Insurance carriers and public sector organizations face their own recordkeeping and information-governance requirements.
But financial services provides some of the clearest and most heavily enforced examples of the compliance risks associated with mobile and off-channel business communications.
Compliance officers, heads of legal and risk, and the technology leaders who support them are the people who need to make the resulting controls work in practice. Getting it right isn’t a checkbox exercise.
The objective is to ensure that business communications can be preserved, supervised where required, and produced in a reliable manner when an examination, investigation, litigation matter, or other legitimate request requires them.
Also Read: WhatsApp Archiving for Business Compliance
Mobile Communications Compliance Requirements
There is no single regulation called “mobile communications compliance.” The requirements come from the rules that apply to the organization and the type of business communication involved.
For financial services, the regulatory connection is particularly clear.
SEC Rule 17a-4 governs broker-dealers and establishes requirements for the preservation of records, including electronic records and communications that fall within the firm’s recordkeeping obligations.
For electronic records, the current rule permits a broker-dealer to use either a non-rewriteable, non-erasable format commonly known as WORM or an electronic recordkeeping system using an audit-trail alternative that can recreate an original record if it is modified or deleted. The rule also contains requirements concerning access to and production of records.
FINRA Rule 4511 addresses books and records requirements for FINRA members, while FINRA Rule 3110 requires firms to establish and maintain a supervisory system reasonably designed to achieve compliance with applicable securities laws, regulations, and FINRA rules.
The exact supervisory procedures and review methods depend on the firm’s business and risk profile. The important point is that preservation and supervision are related but distinct obligations. Keeping a communication does not, by itself, satisfy every supervisory responsibility that may apply to it.
Investment Advisers Act Rule 204-2 establishes recordkeeping requirements for registered investment advisers. Depending on the adviser and the records involved, those requirements can extend to electronic communications relating to the firm’s advisory business.
None of these rules were rewritten to specifically name WhatsApp, iMessage, or every other messaging application in existence. The important issue is whether the communication falls within the firm’s applicable recordkeeping obligations.
The regulatory framework therefore has to be applied to the substance and context of the communication rather than assuming that an approved or prohibited application list, by itself, resolves the issue. There is also a jurisdictional layer worth understanding, particularly for firms with international operations.
Data protection frameworks outside the United States can impose their own requirements around how personal information inside a business message is handled, retained, accessed, and eventually deleted.
A defensible mobile compliance program has to reconcile record-retention obligations with privacy, security, and data-minimization requirements rather than treating them as entirely separate problems.
Also Read: Enterprise iMessage Compliance: How to Archive iMessages
Why Off-Channel Communications Remain a Top Compliance Risk
Off-channel communication is the term commonly used for business communication conducted through channels that are outside a firm’s approved, supervised, or recordkeeping environment. It has become one of the most heavily scrutinized recordkeeping issues in financial services, and the enforcement record makes clear why.

The enforcement wave that shaped this issue began with the discovery that employees were routinely conducting business over personal messaging applications that firms had not approved or captured.
What made the resulting cases notable wasn’t the existence of a few employees texting clients. It was the scale of the behavior across firms and levels of seniority, including personnel responsible for compliance and supervision.
The SEC continued this enforcement initiative through fiscal year 2024. The Commission reported that its off-channel communications initiative had resulted in charges against more than 100 firms and more than $2 billion in penalties since December 2021, including more than $600 million in civil penalties against more than 70 firms during fiscal year 2024 alone.
The lesson is not that regulators are looking only for a particular application. It is that firms need reasonable controls for identifying business communications, preserving records that are required to be maintained, and supervising communications in accordance with their applicable obligations.
That distinction matters for how a compliance program should be designed. A program built only to respond to a major enforcement sweep is not the same as a program designed to withstand an ordinary examination.
The stronger approach is one that continuously addresses how communications are captured, preserved, reviewed, and produced rather than assuming that a written policy will prevent every employee from using an unapproved channel.
A related lesson from the enforcement environment is the importance of remediation. When a firm identifies a recordkeeping or supervisory weakness, the response matters. The SEC has expressly highlighted self-reporting, cooperation, and remediation as factors that can affect enforcement outcomes.
The practical takeaway is straightforward: discovering a gap should trigger action, documentation, and remediation rather than simply adding the finding to an internal list.
The Difference Between Message Capture and True Compliance
This is the part almost every resource on this subject glosses over, and it is the part that actually determines whether a firm has a defensible recordkeeping architecture.
Capturing a message and preserving a message are not the same act, even though the two get used interchangeably in casual conversation. A backup exists primarily to help recover data after something breaks. A recordkeeping system must preserve applicable records in a manner that satisfies the relevant regulatory requirements and supports their retrieval and production when needed.
The distinction matters in practice. Mobile capture solutions can pull messages from supported devices, carriers, or messaging applications and preserve them in a structured format. That is necessary when the communication itself needs to enter the firm’s recordkeeping environment.
But capture is only the beginning. Once a mobile message has been captured, the firm needs controls around what happens to it afterward. Depending on the applicable requirements, that can include enforcing retention policies, protecting records against unauthorized alteration or deletion, supporting legal holds when preservation obligations arise, maintaining appropriate audit information, and making records available in a usable format when they are requested.
This does not mean every firm must place every record in one system. A compliant architecture can contain multiple systems if those systems are appropriately governed and the firm can demonstrate that its required records are being preserved, supervised, and produced as applicable.
The practical problem with fragmented environments is therefore not simply that there are multiple repositories. It is that disconnected repositories can make it harder to apply consistent governance, understand where records reside, reconcile retention requirements, respond to legal holds, and produce a complete set of responsive records.
The issue is rarely just “we didn’t capture the message.” It can become “we captured it, but we cannot reliably demonstrate how it was preserved, locate the complete communication history, connect it with related records, or produce it efficiently when required.”
Mobile Communications Compliance Best Practices for Regulated Firms
A defensible program rests on four connected pillars, and they need to function as one governance framework rather than four separate initiatives.
- Policy that defines permitted channels and required controls. A written supervisory procedure should establish which communications channels may be used for business and what capture or recordkeeping controls apply to them. A prohibition can be useful, but it does not eliminate the need to understand and address how business communications are actually occurring.
- Capture at the device and channel level. Whether a firm issues corporate devices or allows personally owned devices, approved messaging channels need an appropriate technical capture mechanism. Programs involving personal devices also need clear boundaries for separating business communications from genuine personal material and for protecting employee privacy.
- Supervision that is actually performed and documented. Where supervisory obligations apply, the firm needs reasonably designed procedures for reviewing communications based on its business, risks, and applicable requirements. Depending on the program, that can involve sampling, targeted review, automated detection, escalation workflows, or other controls. The review process itself should be documented sufficiently to demonstrate that the firm’s supervisory procedures are operating as intended.
- A coordinated retention and legal-hold framework across channels. Mobile messages, email, and other business records do not necessarily require identical retention periods. They do, however, benefit from a coordinated governance framework that clearly identifies applicable retention rules and ensures that preservation obligations, including legal holds where appropriate, are reflected across relevant repositories.

Underneath all four pillars sits a decision that firms often treat as purely technical but is really a governance decision: where the records reside, how their lifecycle is controlled, and whether the organization can answer an examiner’s question efficiently rather than reconstructing the answer manually from disconnected systems.
Common Mistakes That Undermine Mobile Compliance Programs
A handful of failure patterns recur across off-channel communications enforcement and broader recordkeeping problems, and most of them trace back to the same root cause.
- Treating a device backup as though it automatically provides the controls required for regulated recordkeeping, and discovering the difference only when a specific communication needs to be located and produced
- Approving a messaging channel in written policy but failing to implement the technical capture and recordkeeping controls needed to support that policy
- Letting mobile records remain isolated from other business records, making a client or regulatory inquiry dependent on manual searches across multiple repositories
- Assuming that a written prohibition on texting eliminates the recordkeeping risk, even when employees continue using text or other messaging applications for business communications
- Reviewing captured messages inconsistently, leaving the firm unable to demonstrate how its supervisory procedures operate in practice
- Applying different retention and preservation processes to different channels without a clear governance framework explaining how the requirements interact
Each of these looks like a technology gap on the surface, but underneath it is a governance problem. The fix is not necessarily a better messaging application. It is an architecture that makes the technically correct behavior easier to enforce and the resulting records easier to govern, search, preserve, and produce.
How Archon Data Store Supports Mobile Communications Compliance
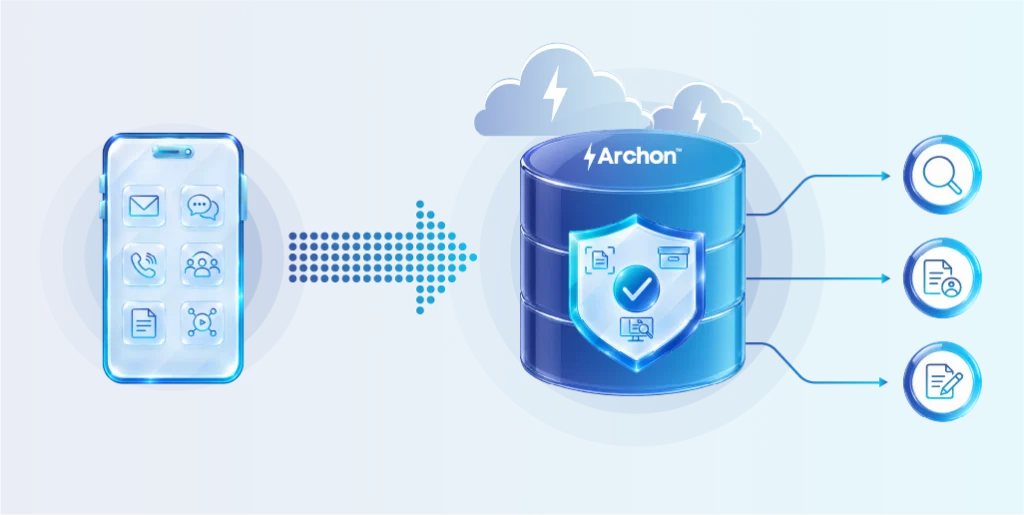
Archon Data Store is not a mobile capture solution, and it doesn’t try to be one. It is the governed archive that can sit beneath existing capture mechanisms, providing a common environment for preserving captured mobile messages alongside email, ERP records, case files, and other enterprise records.
In practice, once mobile messages are captured through an appropriate capture mechanism, Archon can apply policy-driven retention and legal-hold controls to those records within the archive.
The important distinction is that Archon provides the governance layer for records after ingestion rather than claiming to replace the channel-specific technology required to capture every messaging application.
Retention policies can be configured around the organization’s applicable requirements rather than assuming that every record needs the same retention period. When a litigation or investigation matter requires preservation, legal-hold controls can prevent affected records from being disposed of under the ordinary retention process.
On the integrity side, Archon’s architecture supports immutable preservation, cryptographic hashing, and audit logging to help establish the integrity and history of archived records. These controls are designed to support a defensible recordkeeping environment by making it possible to demonstrate how records have been preserved and what actions have been taken within the archive.
The distinction that matters most to a compliance officer, though, is unification. Because Archon can connect to multiple enterprise systems and provide a common metadata-driven search layer, a request involving a particular account, employee, matter, or period can be investigated across connected sources without requiring every record to be physically stored in the same originating application.
That is an architectural advantage, not a regulatory requirement. Firms can operate compliant environments with multiple repositories. The value of a governed enterprise archive is that it can reduce the operational complexity of managing those records across the broader lifecycle.
For firms handling especially sensitive mobile or client material, Archon’s isolated storage environment can provide an additional layer of separation for archived records while keeping governance and retrieval within the same broader archive framework.
| Capability | Mobile Message Capture Solution | Governed Archive like Archon Data Store |
|---|---|---|
| Primary function | Captures business messages from supported devices, applications, or communication channels | Preserves, governs, searches, and produces archived records across connected systems |
| Retention management | Primarily manages or passes captured messages into the applicable retention environment | Applies policy-driven retention controls to archived records across connected sources |
| Legal hold | Capabilities vary by solution and implementation | Provides centralized legal-hold controls for records within the archive |
| Record integrity | Capabilities vary by provider | Supports immutable preservation, cryptographic hashing, and audit logging |
| Search and retrieval | Primarily searches captured communications | Searches mobile communications alongside other connected enterprise records |
| Examination response | May require searches or exports from multiple systems | Enables cross-system search and export across connected archived records |
Conclusion: Building a Defensible Mobile Communications Compliance Program
Mobile communications compliance was never simply a technology problem. It is a governance problem that technology can either mask or genuinely solve.
Capturing the message is essential, but it is only the beginning. A defensible program also needs to address how applicable records are preserved, how retention requirements are enforced, how legal holds are handled when necessary, how communications are supervised, and how records can be located and produced when regulators, investigators, auditors, or legal teams require them.
The objective is not to force every communication into one application or claim that one technical architecture is mandated by regulation. It is to make sure the organization knows which communications it is required to preserve, has appropriate controls around those records, and can demonstrate that those controls work.
For firms managing mobile communications alongside email and other enterprise records, a governed archive can provide the common layer needed to bring those records into a consistent lifecycle without replacing the capture systems responsible for collecting them. That is the layer worth getting right before the next examination letter arrives, not after.


